


Let's talk about the difference between ISO27001 and ISO27002 for a while. First thing to mention between the two of them is that one is a management standard, that you can certify against, and one is not.
ISO27001 is a management standard that defines how to run a system. In the case of ISO27001 it's the Information Security Management System, or ISMS. It helps establish, maintain, and continually improve an ISMS against the international standard. As such certification against ISO27001 is possible.
Every standard in the ISO27000 series has a specific focus. If you want to build an ISMS framework and foundation you start with ISO27001, but if you want to implement controls you look to ISO27002.
In Annex A of ISO27001 there are control objectives aligned with ISO27002. But before I go any further, I should point out that there has been a revision of ISO27002 that has yet to be aligned with Annex A in ISO27001. It's why you will see ISO27002:2022 out there whilst utilizing ISO27001:2013.
Back to the differences though between the two, it comes down to the level of detail between Annex A in ISO27001 and ISO27002. ISO27002 is more precise, and detailed, providing implementation guidance and other information along with the control. Because ISO27001 requires a risk assessment to be performed to determine if a control is required to reduce risk, and the extent to which it should be applied, not all controls may end up applying to your organization. ISO27002 doesn't make that distinction.
So, in summary if you want to construct the foundations of information security for your organization, define a framework and achieve certification you should use the ISO27001 management standard. If you want to implement controls, you should refer to the more detailed ISO27002.



Related Blogs
Stay up-to-date on the latest happenings in Cybersecurity and PCI Compliance.
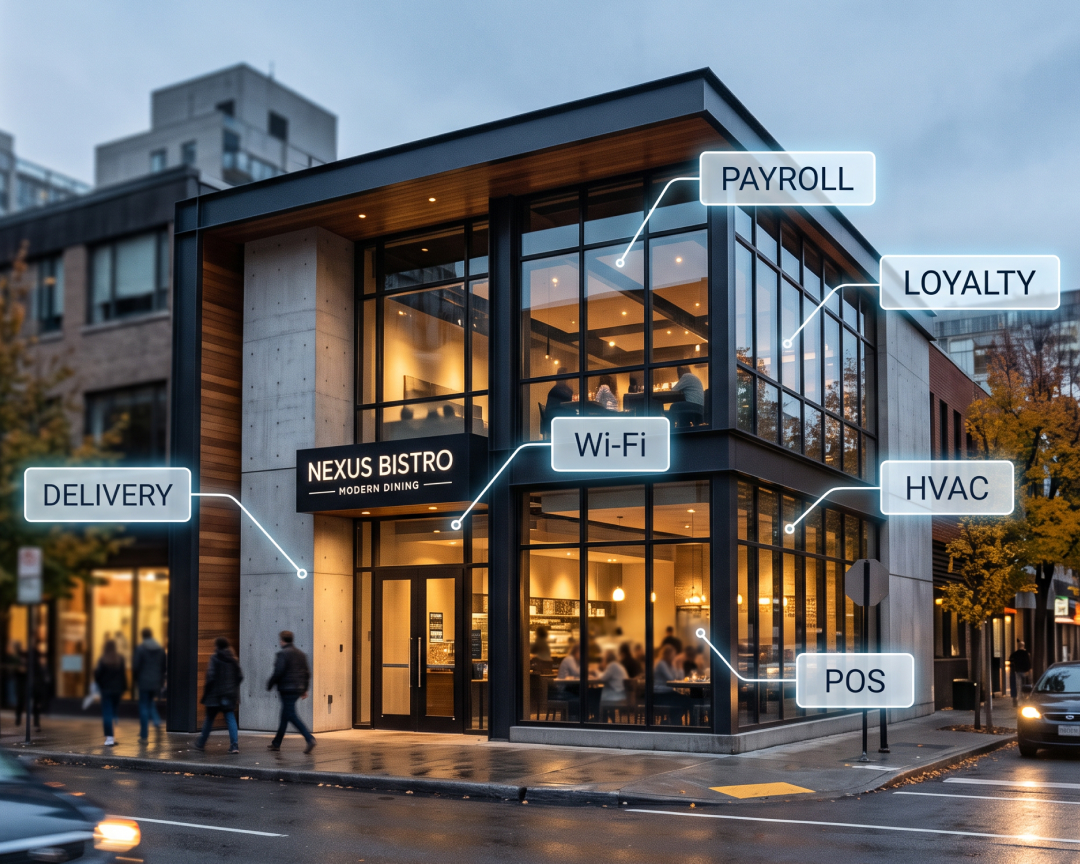
Third-Party Vendors Already Have Access to Your Stores. Are You Managing the Risk?
