VikingCloud News & Resources
Check out the latest news and resources from VikingCloud.
Explore all Resources
Your teams are using AI tools you may not know about. Your vendors are switching on AI features without asking. Now your customers, your board, and your regulators want proof of who’s in control. VikingCloud AI Governance Services find the AI in use across your business, score how well it’s governed, and give you a prioritized plan to close the gaps.
Whether you’re still building your AI governance or ready for an independent audit, there’s a clear next step.
Path 1 · Advisory
See where your AI governance falls short and what to fix first. We review how your organization uses and governs AI and give you a prioritized plan. This is an advisory assessment, not a certification.
Path 2 · Certification
If your AI management system is in place, an independent certificate proves it conforms to ISO/IEC 42001. VikingCloud Audit & Certification, LLC, a separate certification body, audits and certifies AI management systems. It does not provide consulting or implementation advice.
Both services use our proprietary assessment model of 10 risk areas and give you evidence you can show your customers and your board. Choose a fast baseline or a full, standards-mapped assessment.
1
Know where you stand in three weeks.
An AI governance specialist reviews how your organization uses AI and tells you, in plain language, what’s working and what needs attention. We interview your teams, map where AI is in use, and run five diagnostic tests, including shadow AI discovery.
What you get:
 An AI Health Index from 0 to 100, with a status for each risk area.A register of where AI must never be used in your business.A 30-, 90-, and 180-day plan with an owner for every action.
Best for: Organizations that know they need to act on AI governance but don’t yet know where to begin.
2
Evidence you can defend.
Our specialists run 101 checks across all 10 risk areas. Each check is documented and mapped to a specific requirement in ISO/IEC 42001, ISO/IEC 42005, the NIST AI RMF, the EU AI Act, or AIUC-1. The result is a position you can defend to customers, regulators, and your board.
All AI Health Check features, and:
Where you stand against each standard, and how much of it your evidence covers.Detailed findings for each risk area, each tied to the requirement it tests.An inventory of your AI systems, ranked by priority, and a register of your AI vendors.A plan you can act on now or use to prepare for ISO/IEC 42001 certification.Best for: Organizations facing customer, regulatory, or contractual pressure to show how they govern AI, and those planning ISO/IEC 42001 certification.
International standard, certifiable
The AI management system: how your organization governs AI across the business.
International standard, guidance
AI system impact assessment: how an individual AI system affects people and society.
U.S. framework, voluntary
Managing AI risk through four functions: govern, map, measure, and manage.
EU regulation, law
Obligations for organizations that provide or use AI in the EU, phased in from 2025 through 2028.
Emerging standard
An assurance standard for AI agents.
Book a free 30-minute consult with an AI governance specialist. Bring your questions and get straight answers before you decide.
VikingCloud’s proprietary assessment model covers 10 risk areas. Can you answer these questions with evidence today?
Do you have an AI strategy with a clear owner, tied to business goals and a defined risk appetite?
For every decision AI influences, is a named person accountable, and can they actually override it?
Do you know what AI is running, including the tools your vendors switched on and the ones your staff adopted on their own?
What data reaches AI tools, and what stops regulated or sensitive data from getting there?
Are access, prompts, connectors, agents, and the AI supply chain protected, and do you have a playbook for an AI incident?
Can you reconstruct a decision AI shaped, with the model version, inputs, and reviewer, months after the fact?
Is AI the right tool for each use case, and are outputs evaluated against accuracy, cost, and risk?
Where should AI never be used in your business, and has anyone written that down?
Which AI capabilities exist in-house, which are missing, and where is a single person a point of failure?
Which AI laws apply to you, and in what role, such as provider or deployer? Are your AI vendors assessed like any other third party?
Built by security assessors
AI governance from the security assessors leading brands trust.
VikingCloud’s proprietary assessment model includes:
To see how the applications and systems your AI runs on hold up against real-world attacks, pair your assessment with penetration testing.

1. Assessment expertise.
Our AI governance specialists bring the rigor and discipline the world's leading brands already trust. They verify what's actually in place, not just what the policy says.

2. Independence by design.
We assess and advise. An independent organization of your choice certifies your AI management system. And we'll tell you exactly where you stand before your audit.

3. One partner, one platform.
Get compliance assessments, security testing, and managed security services from a single provider, with your AI governance findings alongside the rest of your program in the Asgard Platform®.
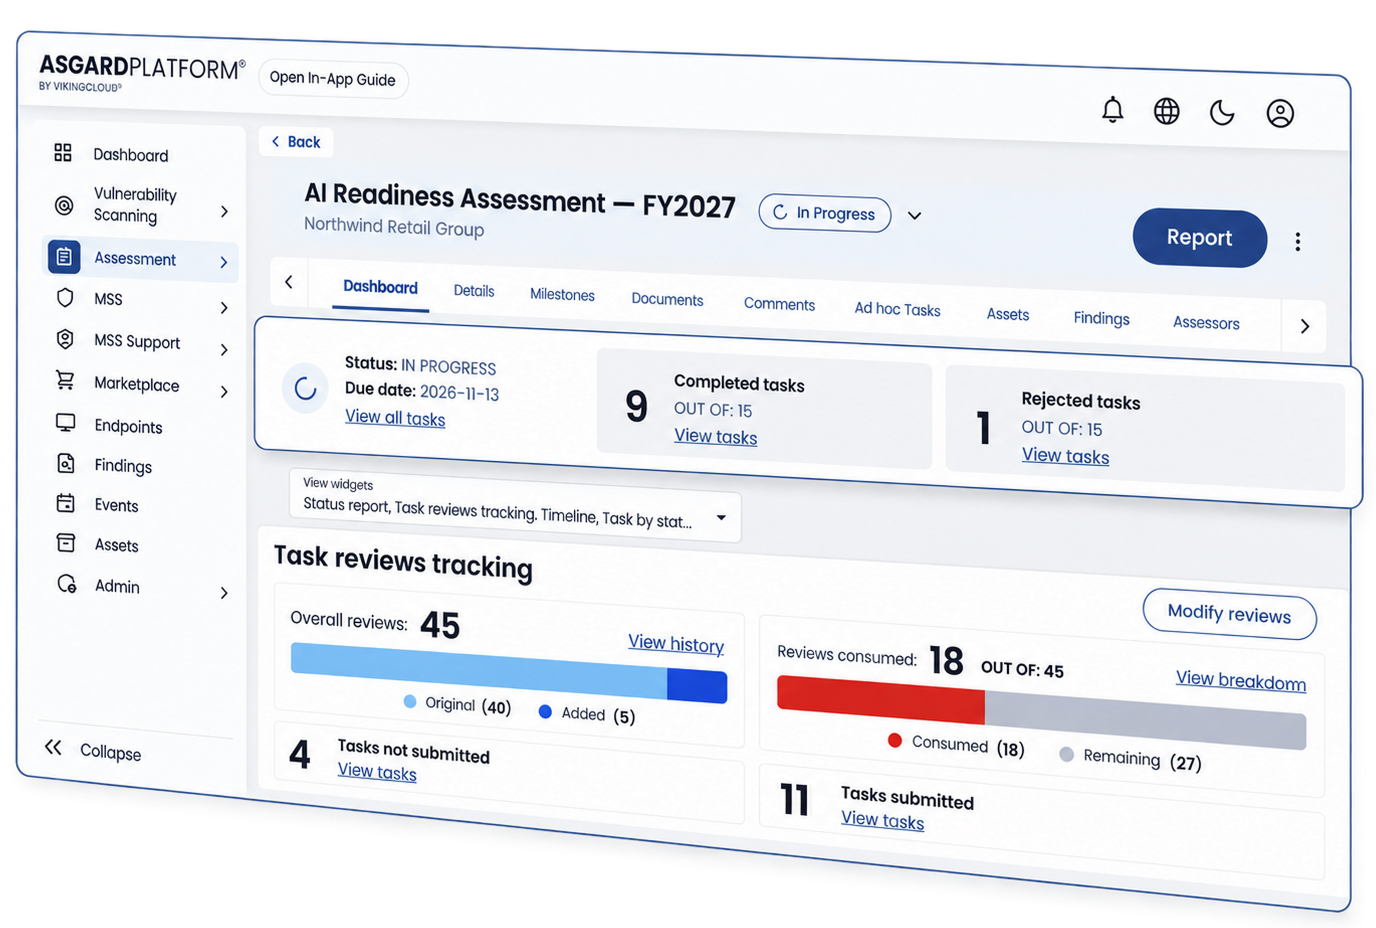
Manage your AI Readiness Assessment in the Asgard Platform.
Your assessment lives in one secure platform, alongside any PCI or other compliance work you manage with VikingCloud.
ISO 42001 Certification
VikingCloud Audit & Certification, LLC is a separate certification body that audits and certifies ISO/IEC 42001 and ISO/IEC 27001 management systems. It makes its own certification decisions, provides no consulting, and does not certify management systems VikingCloud has advised on.
Get the details on the AI Health Check and AI Readiness Assessment. To find out more about VikingCloud’s full suite of cybersecurity and compliance services, view all our datasheets.
AI governance sets the rules for how your organization uses AI. It defines the policies, accountability, and oversight for issues like bias, privacy, and compliance, often guided by frameworks such as ISO/IEC 42001.
AI security uses technical controls to protect your AI systems from threats and vulnerabilities such as prompt injection, data poisoning, and data leakage.
Governance asks, “Should we use AI this way, and who’s accountable?” Security asks, “How do we stop it from being misused or attacked?” You need both to use AI responsibly.
An AI risk assessment identifies and evaluates the threats and vulnerabilities your AI systems could introduce. It reviews how you use AI, what data it accesses, and where issues like bias, privacy exposure, security gaps, or noncompliance could affect your business.
The result is a clear set of findings and prioritized recommendations, so you can address the most serious issues first and strengthen your AI governance and security. It’s also a core requirement of ISO/IEC 42001.
No. It’s an advisory assessment that shows how close you are to the standards that apply to you and what to do about the gaps. Certification is a separate, independent audit by a certification body you choose.
No. Independence is what gives a certificate its value. VikingCloud’s affiliated certification body, VikingCloud Audit & Certification, operates separately and does not certify management systems that VikingCloud advised on.
Maybe not yet. The AI Readiness Assessment covers five frameworks, so you’ll learn which ones your customers, partners, and regulators expect before you commit to a standard.
If you provide or use AI in the EU, it may. Some obligations already apply, and most transparency rules took effect in August 2026. Obligations for high-risk AI systems, such as AI used in hiring, credit, or access to essential services, apply from December 2027; AI built into regulated products like medical devices follows in August 2028. The AI Readiness Assessment maps your practices to the Act, so you know where you stand.
A conversation with one of our AI governance specialists about the questions you have. It’s not the assessment, and there’s no score. It’s a way to get straight answers before you decide what you need.
The AI Health Check takes two weeks after a one-week intake. The AI Readiness Assessment takes four to six weeks with three days of fieldwork, and less when you’ve had the Health Check first.
No. It shows where you stand and how to close the gaps. Independent certification is how you prove conformity to a standard like ISO/IEC 42001.
Check out the latest news and resources from VikingCloud.
Get started with a VikingCloud cybersecurity and compliance assessment with our cybersecurity experts.