Walk through one of your locations, and you'll spot plenty of tech that isn't on your IT team's procurement list.
The refrigeration contractor set up remote monitoring years ago. Facilities added smart HVAC controls during a remodel. Marketing rolled out digital signage. Operations deployed self-service kiosks. A telecom provider swapped out the network during an internet upgrade. Along the way, security cameras, badge readers, and vendor-managed devices quietly joined the network.
Each choice made sense on its own. Together, they've built a web of tech that's hard to see in full. In our work with multi-location retailers, we rarely encounter a team that can confidently list every connected device.
Technology has expanded faster than governance.
A decade ago, a typical retail site was easy to grasp: a point-of-sale system, a few employee workstations, payment terminals, and a router made up most of the tech.
Today's locations look very different.
Customer experience initiatives, energy management projects, remote monitoring, and operational efficiency programs continue to add connected devices to your stores. IoT Analytics counts 21.1 billion connected Internet of Things (IoT) devices worldwide at the end of 2025 and expects 39 billion by 2030. More and more of them sit in commercial spaces like yours, and the trend shows no sign of slowing.
The challenge isn't poor technology decisions. Each new project added one more layer of gear, and no one was asked to map the whole picture. The result: infrastructure nobody signed off on, and no one is accountable for it as a whole.
The visibility gap isn't an IT problem.
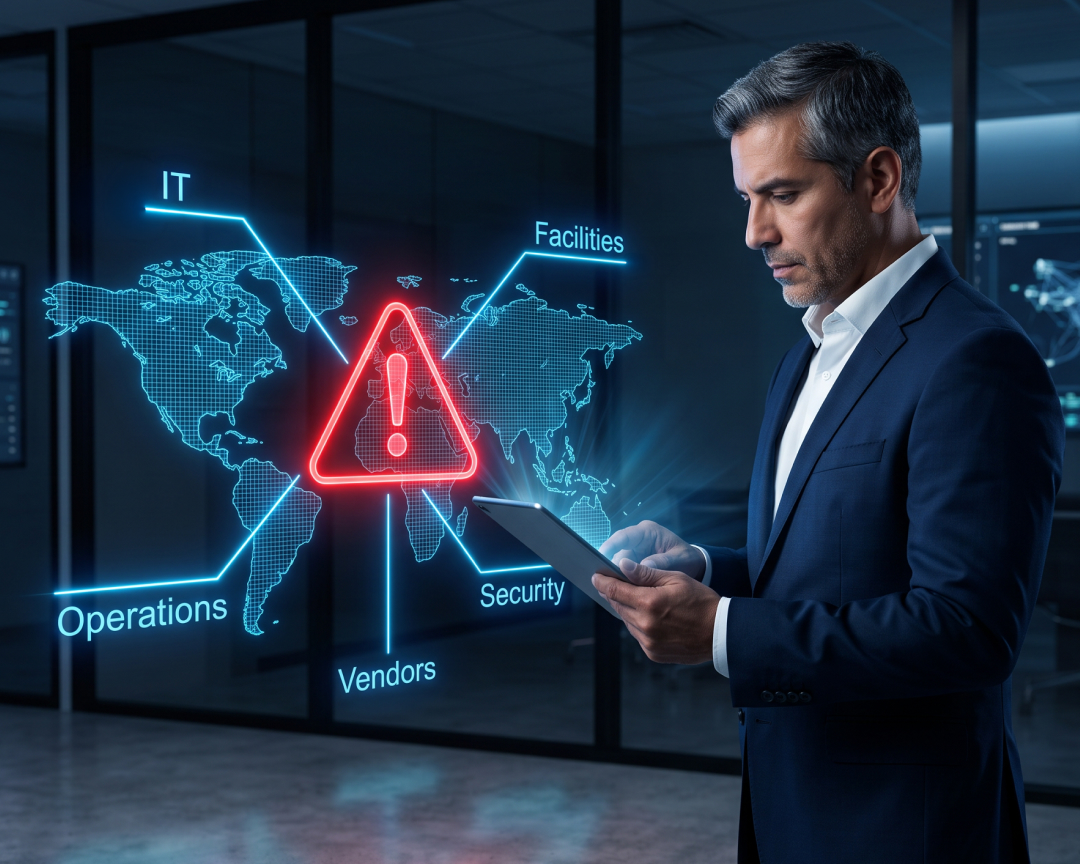
Ask who owns device visibility across your sites, and you'll hear a different answer from each team.
IT points to endpoints and networking equipment. Facilities claim building systems. Operations owns kiosks and tablets. Security sets the policies. Vendors maintain the systems they installed.
Each group owns a piece, and no one owns the whole. That gap matters because uptime depends on how these systems work together, not on how each team runs its own slice. The National Institute of Standards and Technology (NIST) saw this too. It added a new Govern function to its Cybersecurity Framework 2.0, stating that risk work begins with clear owners before any technical control is applied. Without a clear owner, gaps stop being one-off slips and become fixed parts of your network. It's tempting to hand all of this to your security team. We'd argue that's the wrong first move.
Treating device visibility as a security project sends it to a team that can't fix what drives it: buying habits, vendor contracts, and facilities upgrades that never pass through IT. Frame it as a governance gap in how you run the business and put it in front of whoever holds authority across IT, operations, and facilities at once. In most firms, that's the COO, CTO, or CEO.
Franchise groups face a harder version of the same gap. Corporate can publish standards, but franchisees buy their own gear and sign their own vendor deals. You carry the duty to govern an estate you don't fully control. That's an authority problem, and policy alone can't close it.
Vendor-managed doesn't mean vendor-owned.
Many of the systems your locations rely on aren't run by your IT team at all. HVAC contractors access equipment remotely, refrigeration vendors monitor temperatures, signage firms push content to screens, and payment providers support the checkout. These ties help, but also create always-on links to each site. The access itself isn't the issue. What matters is whether anyone reviews it: who has it, why, and when it should end (and this is just the access; not to mention patching, security, compliance and other requirements). Most third-party risk programs are built to catch this in a contract or a questionnaire. The access is already live within your network and at your locations, whether or not it ever shows up in a vendor review.
The 2026 Verizon Data Breach Investigations Report found that breaches involving a third party increased 60% year over year and now account for 48% of all breaches. In plain terms, when things go wrong, a partner link is part of the story nearly half the time. If you rely on dozens of vendors across hundreds of sites, each of those links deserves the same review as the gear you manage yourself.
One flat network turns small faults into outages.
At most sites, all this gear shares a single network. Cameras, HVAC controllers, and point-of-sale terminals often sit on the same segment with nothing between them. That's rarely a design choice. It's what happens when systems arrive one at a time with no rule about keeping them apart. On a flat network, a single failing or compromised device has a direct path to everything else at that site, and a contained device problem can become a full store outage.
Device visibility is what keeps your doors open.
You can't maintain what you can't see, and that truth reaches well beyond cybersecurity. If you can't answer basic questions about a site (what's connected, who installed it, who supports it, which vendors can reach it from afar, and which systems are near the end of life), you're deciding with half the facts. The PCI Security Standards Council continues to expand its rules on asset inventory, network security controls, and ongoing monitoring in PCI DSS v4.0.1 for the same reason: protection starts with knowing what's there. We also see cyber insurers ask for the same evidence at renewal: a current asset inventory and proof that store systems are kept apart. Visibility also speeds up recovery.
When a location experiences an outage, knowing exactly what's installed helps your team find the fault faster, call the right vendor sooner, and reopen with confidence. Without that knowledge, troubleshooting turns into guesswork.
Where to start.
You don't need a formal assessment to test whether this gap exists in your business. Ask one question: do we know what's connected across our locations, who installed it, who's responsible for it, and whether it's still supported? If the answer is shaky, here's the order we recommend.
- Name an owner first. Pick who's accountable for device visibility across IT, OT, facilities, and vendor-run systems before you buy any tool. Tools without an owner don't get acted on.
- Build one inventory that includes both IT and non-IT gear. Cameras, HVAC controllers, refrigeration monitors, signage, kiosks, and anything a vendor manages all count.
- List every outside party with standing access. Note the credentials they use and when the last access was reviewed. No list? That's your first finding.
- Check the network layout at each site. Find out whether store systems share segments or sit apart. When nobody knows, assume they share.
- Flag every device past vendor support. You don't have to replace them all this year, but you do have to know which ones have no patch path and no owner.
Two traps to avoid: don't route this to security alone, and don't assume your current tools or managed service provider already cover it. Most discovery and endpoint tools were built for laptops and servers, not for OT and IoT gear, and many service contracts exclude vendor-run systems from scope. Verify coverage in writing before you count on it.
Where VikingCloud comes in.
Your customers don't care whether an old device, a vendor-run system, or a network fault caused the outage. They only know the store stopped working.
The businesses that bounce back fastest know their sites well enough to make good calls under pressure.
At VikingCloud, we help retailers, restaurants, hospitality brands, healthcare groups, and other multi-location businesses win back that visibility through managed network services built for uptime. We blend network oversight, device visibility, and 24/7 support, so you always know what's running at every site, and your locations stay open for business.
Our Managed Detection & Response (MDR) service extends that watch into OT and vendor-run systems that standard endpoint tools miss, so we spot trouble at the edge early rather than after an outage.
Contact us to learn more.



Related Blogs
Stay up-to-date on the latest happenings in Cybersecurity and PCI Compliance.
Leading from the Front: Why ISO/IEC 42001 Is the CISO's Next Strategic Advantage