
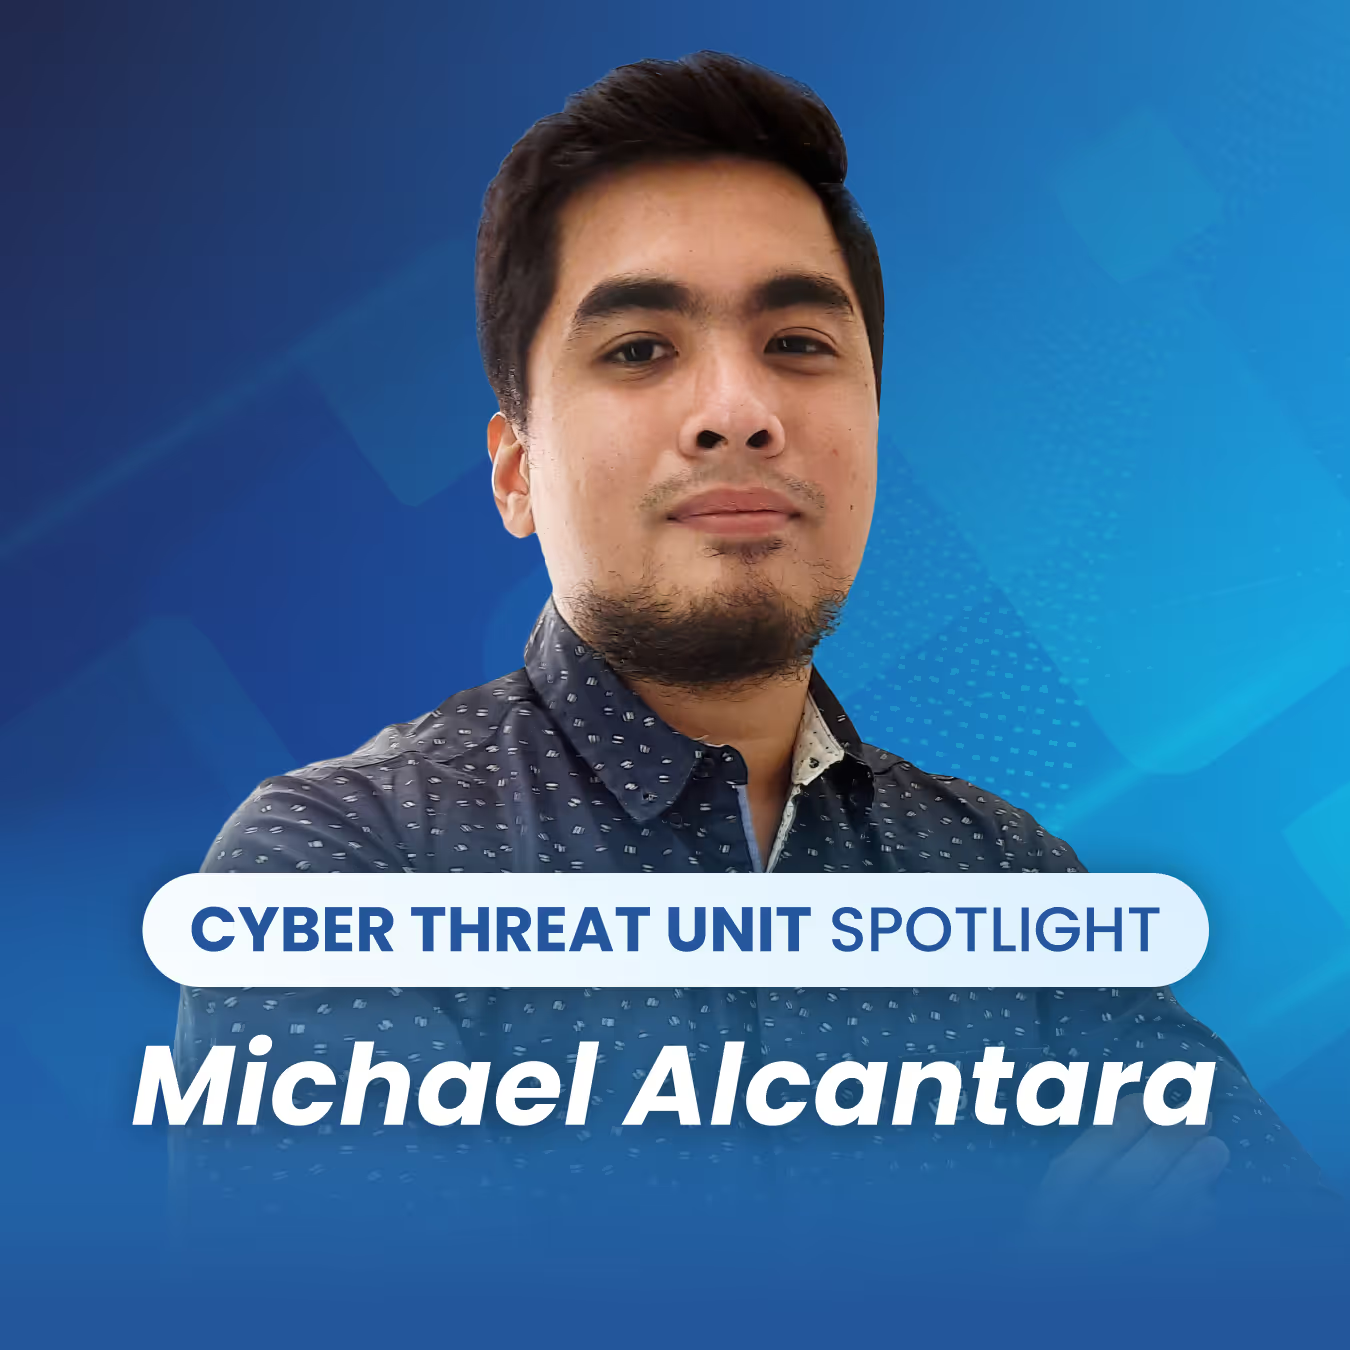
Offensive Security Engineer | Mobile App Security Expert | Team Leader
Michael leads Vulnerability Assessment and Penetration Testing (VAPT) across web applications, mobile apps, and network environments. His work focuses on what matters most: finding real security gaps, simulating real-world attacks, and delivering clear, actionable guidance that helps clients strengthen their security posture fast.
He doesn’t just test systems. He thinks like an attacker, helping organizations understand where they are exposed and what to fix first.
Leadership Through Depth and Precision
Michael plays a key role in leveling up the team. He mentors peers through hands-on guidance, technical deep dives, and knowledge-sharing sessions that raise the bar across every engagement. His leadership helps ensure consistency, quality, and confidence in every assessment we deliver.
Deep Expertise in Mobile SecurityMichael specializes in mobile application penetration testing, leading advanced Android and iOS assessments and training teammates on modern mobile attack techniques. Outside of client work, he conducts independent research into mobile threats, reverse engineering, and exploitation tools. He is also active in security communities and Capture the Flag (CTF) challenges focused on mobile security.
This constant hands-on learning keeps his skills sharp and his insights relevant.
Education & Training
- Bachelor of Science in Information Technology, Quezon City University.
- Specialized training in web application penetration testing through Rootcon, one of the largest hacking conferences in the Philippines.
Q&A with Michael Alcantara
What’s the most common cause of breaches?
Misconfigurations, weak authentication, and insecure coding practices. In web and mobile apps, that often means poor access controls, missing input validation, or exposed APIs. These issues make it easier for attackers to bypass authentication, escalate privileges, and access sensitive data.
What’s your top piece of advice?
Treat security as an ongoing discipline, not a checkbox. Many organizations still approach security only when an audit is due. Attackers don’t operate on audit schedules. Real protection comes from building security into everyday development and operations.
A real-world example?
During a mobile penetration test, I found sensitive data stored in plain text on a device. The client initially viewed it as low risk since no card data was involved and encryption was planned later. After I demonstrated how easily the data could be extracted and abused, the risk became clear. Fixing issues early in the development cycle is far safer than postponing them.
Why Michael Matters
Michael combines deep technical expertise with calm, credible leadership. He raises the performance of the team around him while delivering assessments that clients trust. His commitment to precision, integrity, and continuous improvement makes him a key part of what sets our offensive security practice apart.



Related Blogs
Stay up-to-date on the latest happenings in Cybersecurity and PCI Compliance.
Harvest Now, Decrypt Later: Why Post-Quantum Deadlines Are Tighter Than They Look
